

None of these APIs use
Authorization: Bearer with a TalkChief key. Bearer and basic auth only apply to webhook deliveries that TalkChief sends to your endpoint.Generate a key
1
Open the API keys
Sign in as a company admin and go to Integrations → API → Overview & keys. Under API Keys there’s one panel for Click-to-Call and one for AI Transcriber.
2
Generate the key
If a panel says No key generated yet., click Generate key. Once the key exists, the panel shows Active.
3
Copy the key
Click Show key to reveal it, or click Copy to copy it. You can come back to this page any time to view the key again.
4
Note your Company ID (transcription only)
The Company ID appears at the top of Integrations → API → Overview & keys. Send it as
company_id with AI Transcription requests.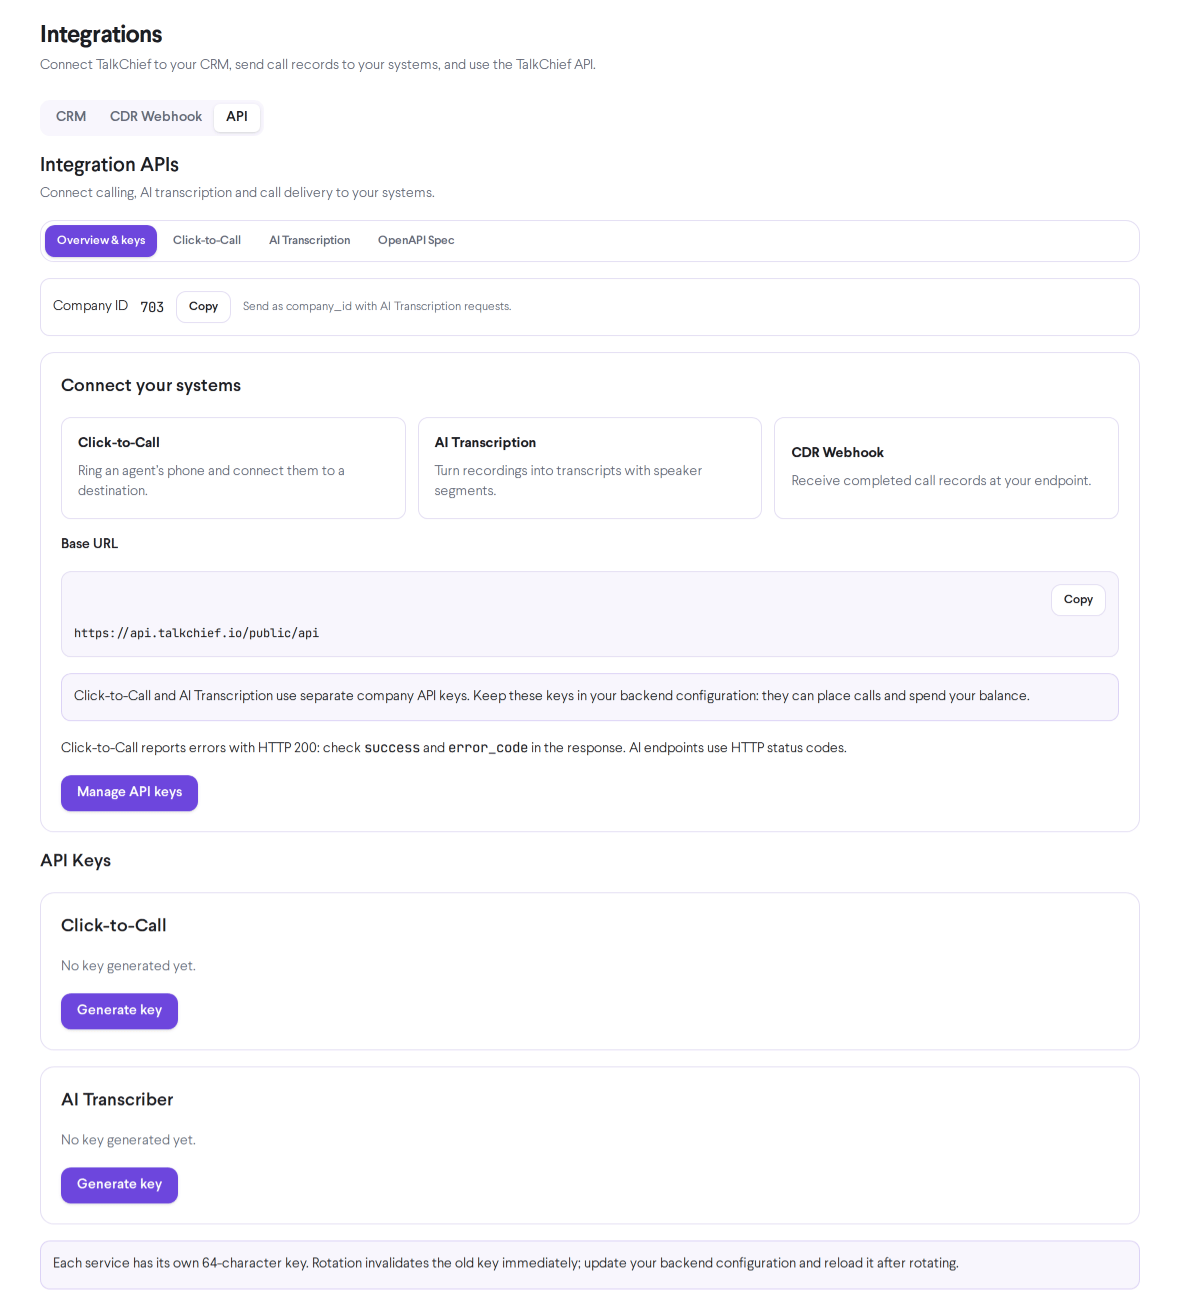
Send the key
api_key in the body and the X-API-Key header together, Click-to-Call uses the body value.
What happens when a key is wrong
The two APIs report key problems differently.
Click-to-Call answers successful calls and the errors above with HTTP 200, so check
success and error_code in the response body. A request that goes over the rate limit is rejected with HTTP 429 before it is processed, so check the HTTP status first. See REST API conventions for both response formats.
Rotate a key
1
Start the rotation
In Integrations → API → Overview & keys, click Rotate key on the panel you want to rotate.
2
Confirm
The dialog warns that the current key stops working immediately. Click Confirm rotation.
3
Update your integration
Copy the new key into your backend configuration and reload it. Requests that still use the old key fail right away.
Security practices
- Keep keys on your server. Never put them in browser JavaScript, mobile apps or public repositories.
- Store keys in environment variables or a secrets manager.
- If you think a key has leaked, rotate it right away.
- For the CDR webhook, use HTTPS and turn on one of the authentication options. Your endpoint can then reject requests that don’t come from TalkChief. See CDR webhook.